ISO 27001 Software

ISO 27001 Information Security Management

Manage information security risks, controls, and audits for ISO 27001 in Nulogy Quality & Compliance. Protect sensitive data, build customer trust, and stay ready for certification.

Protect customer dataImprove security processesWin security-conscious customers
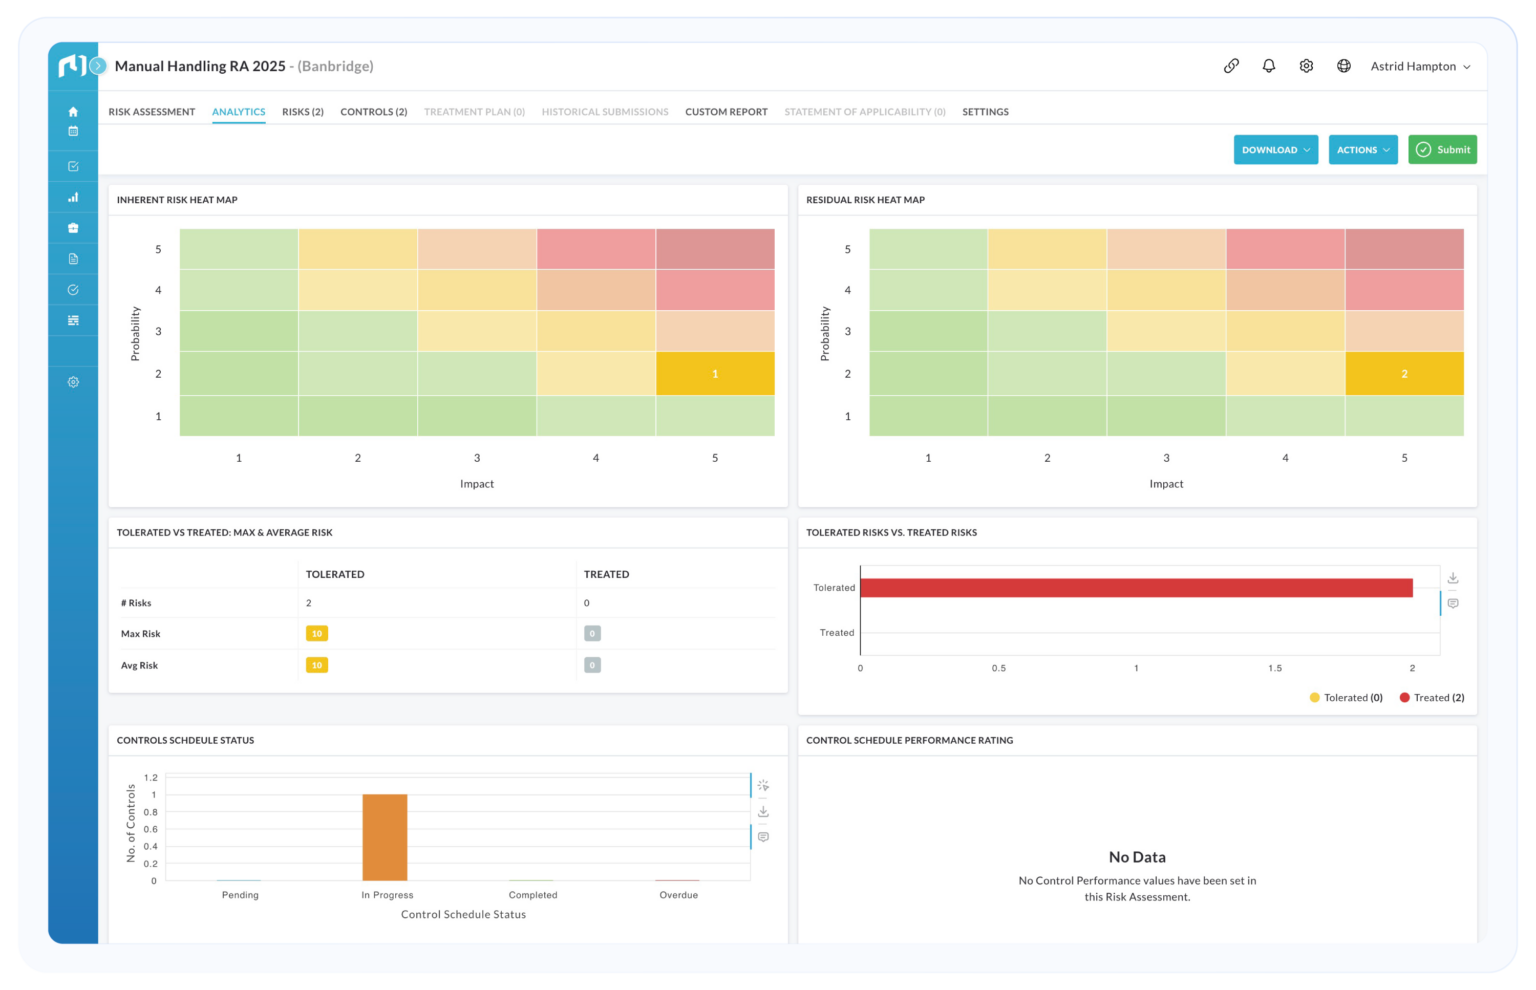
Inherent and residual risk heat maps
Strengthen your security position

A proactive, security-first approach to ISO 27001

Nulogy brings audits, risks, controls, and certifications for your information security management system (ISMS) into one place. See exposure clearly, act on it early, and show auditors the evidence behind every control.

Learn more about Quality & Compliance →

01

Centralize risk tracking

Identify and mitigate risks in real time, with automated workflows that keep decisions moving.

02

Build ISO 27001 audit templates

Run risk assessments, audits, and compliance checks from templates that surface vulnerabilities.

03

Link risks, controls, and assets

Map risks to the controls and assets they affect, so nothing sits in a silo.

Trusted by manufacturers worldwide, from food to industrial
Henderson GroupLakelandDHL Supply ChainMcCloskey InternationalTESABLippmann
Capabilities

Risk oversight for your ISO 27001 program

Move off spreadsheets to a structured approach with full visibility of information security risk.

Risk assessments with automated workflows

Automate risk identification, assessment, and mitigation with custom workflows.

Risk visualization and KRI tracking

Dashboards, automated reporting, and key risk indicator (KRI) tracking for early warning.

Risk exposure across assets

Assess risk impact and dependencies across infrastructure, processes, and suppliers.

Risk register

A central register of risks, categorized by severity and owner.

Risk control and treatment

Map risks to controls, track control performance, and test effectiveness.

Vendor risk management

Monitor third-party exposure and track vendor compliance with your requirements.

Document library

Store and control security policies, procedures, and evidence in one place.

Incident notifications and alerts

Track incidents with automated alerts and response workflows.

Framework compliance

Update risk assessments as regulations and frameworks change.

Risk, policy & control

One library for risks, policies, and controls

Connect each risk to the policies, controls, and evidence behind it, with full lineage and traceability. Stay aligned with industry frameworks and walk into audits with the evidence already linked.

Risk and control lineageTrack dependencies between risks, policies, and controls.
Unified libraryFrameworks in one place, updated centrally.
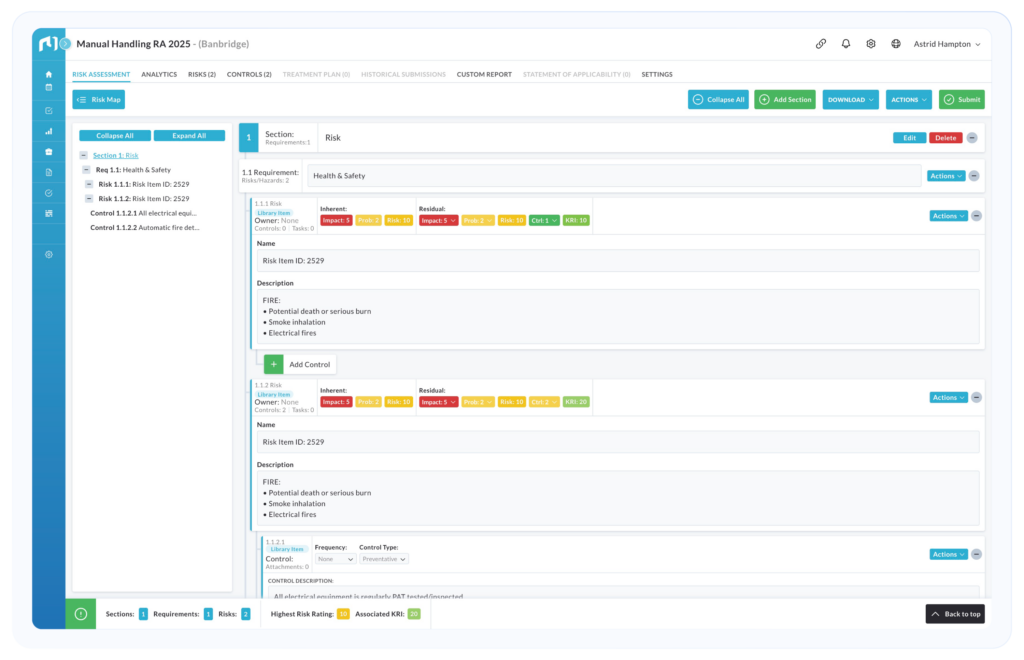
Risk assessment with inherent and residual scoring
Risk visualization

Clear insights, stronger security decisions

Heat maps, risk matrices, and automated reports show threats, control effectiveness, and compliance gaps at a glance. Roll risk up across every asset and get alerted when a control fails.

Interactive risk dashboardsSee exposure, trends, and mitigation progress.
Automated risk reportsReal-time insights for stakeholders.
Risk roll-upExposure aggregated across all assets.
Control statusAlerts when controls fail.
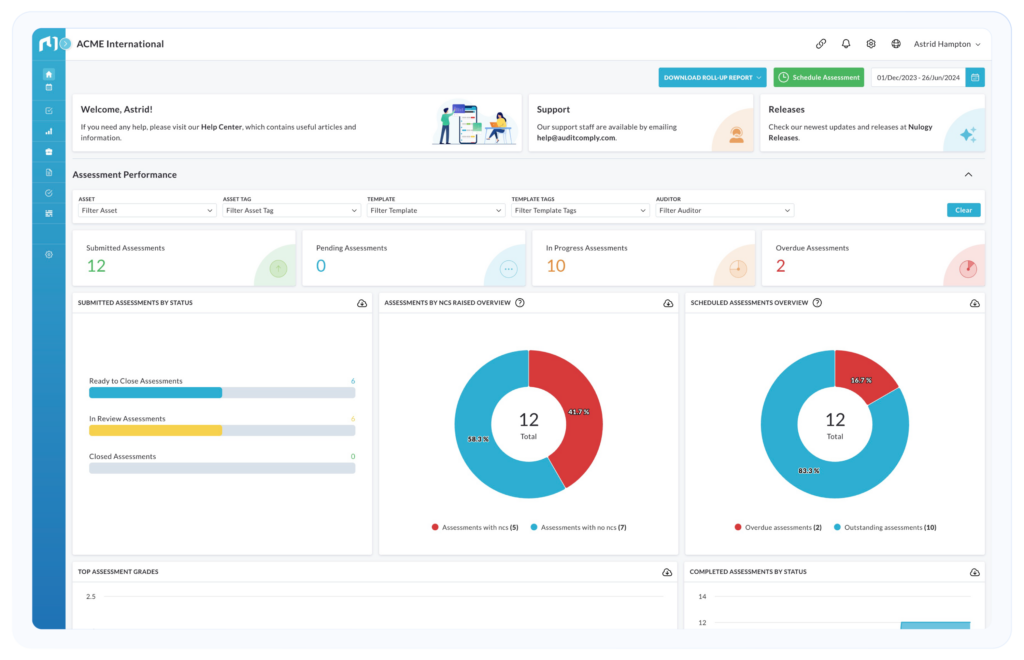
Nulogy Quality & Compliance assessment performance dashboard
Access control

The right access for every role

Role-based permissions control who can view, create, and edit templates, schedules, and reports, so sensitive information stays with the people who need it.
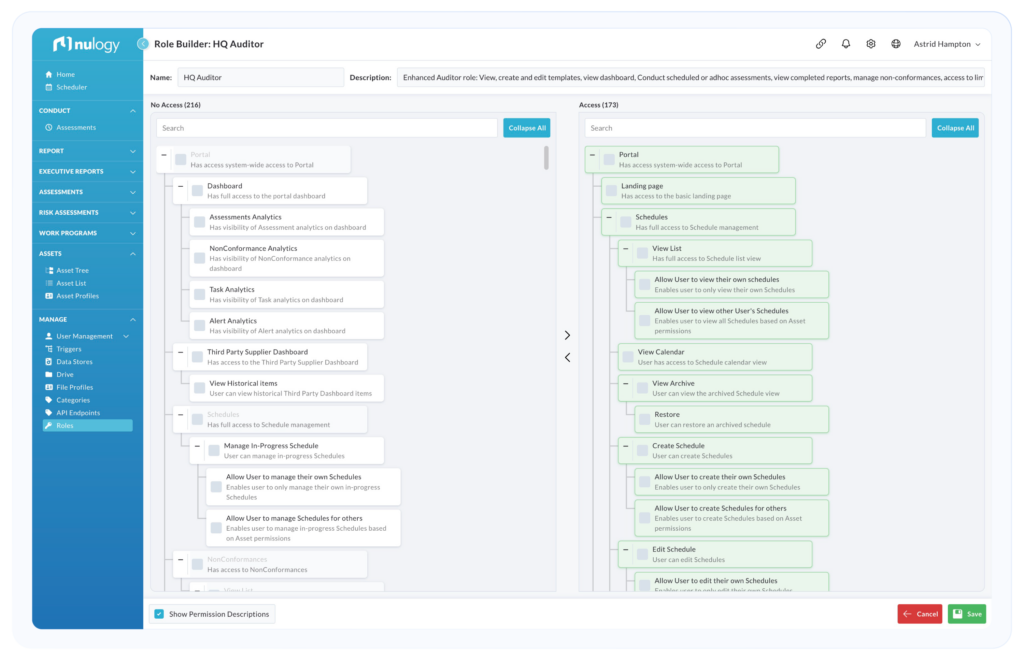
Role-based access permissions
“
Nulogy offers much more flexibility than our previous processes, enabling more insight and instilling confidence that things have been done the right way. Nulogy’s capturing and reporting ability saves time and proves to be a better, more robust way of doing things.
Michael Surginor, Commercial Manager, Henderson Group
FAQ

Frequently asked questions about ISO 27001

How ISO 27001 works, and how Nulogy supports it.

What is ISO 27001, and why is it important?

ISO 27001 is the internationally recognized standard for managing information security. It provides a framework for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). Certification shows a company is committed to safeguarding sensitive data, builds trust with stakeholders, and reduces the risks that come with cyber threats.

What are the key requirements for ISO 27001 certification?
  • Conduct a risk assessment to identify threats and vulnerabilities.
  • Develop and implement an ISMS with controls that mitigate those risks.
  • Document information security policies and procedures.
  • Train staff on security protocols and their roles.
  • Pass an independent audit by a certification body.
How long does it take to achieve ISO 27001 certification?

It depends on the organization’s size, complexity, and current security practices. Small and medium-sized organizations typically achieve certification in 6 to 12 months, including gap analysis, ISMS implementation, internal audits, and the certification audit.

What are the benefits of ISO 27001 certification?
  • Stronger data security and lower risk of breaches.
  • Compliance with legal and regulatory requirements.
  • More trust from customers and stakeholders.
  • An advantage when bidding for contracts where information security matters.
  • Clearer internal processes through documented procedures and defined roles.

Ready to Simplify ISO 27001 Compliance?

Talk to our team about running ISO 27001 in Nulogy Quality & Compliance, from your first risk assessment to your certification audit.

Working to a different standard? See all frameworks.